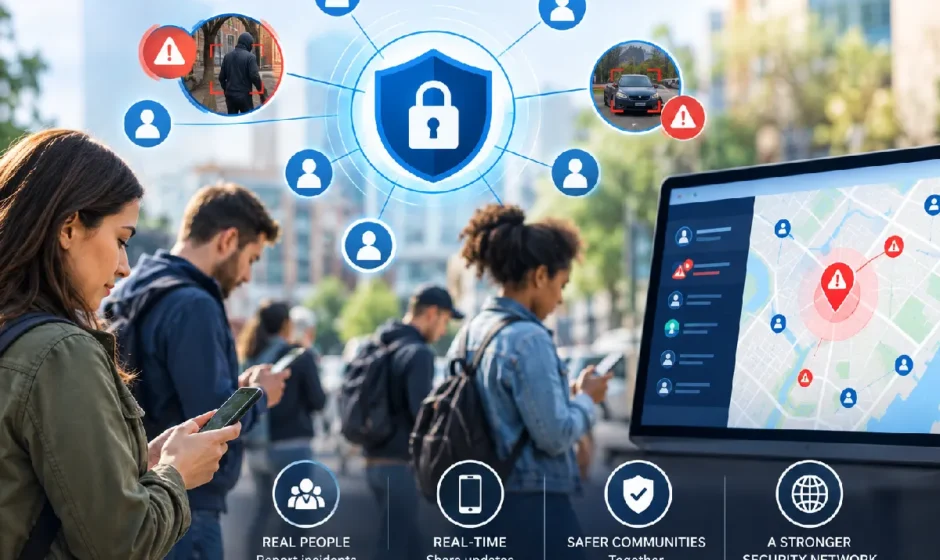
Crowdsourced security testing draws on a distributed network of independent researchers rather than a single fixed internal or vendor team, and it has moved from a niche approach to a genuine sourcing model businesses actively weigh against traditional options. This piece covers what crowdsourcing actually changes about coverage and cost, the vetting and liability questions buyers reasonably ask before adopting it, and where a dedicated internal or vendor team still wins outright.
What Does Crowdsourcing Actually Change About Coverage and Cost?
A traditional testing engagement, whether internal or through a single vendor, draws on a fixed pool of testers with a specific, limited range of expertise and perspective. Crowdsourced testing instead draws on a much larger and more varied pool, meaning an organization gains access to a wider range of specialized skills and, often, a more diverse set of approaches to finding the same vulnerability than any single fixed team would bring.
AI pentesting sits alongside crowdsourced approaches as part of this same broader shift in sourcing models, both departing from the traditional fixed team structure in favor of drawing on capability that scales differently than a single dedicated group ever could.
Cost structure shifts accordingly too. Rather than paying for a fixed team’s full-time capacity regardless of actual testing need, crowdsourced models typically price based on actual findings or engagement scope, which can align cost more closely with genuine risk reduction than a flat retainer model does.
What Vetting and Liability Questions Do Buyers Reasonably Ask?
Drawing testing capability from a distributed network of independent researchers rather than employees or a single contracted vendor raises legitimate questions that a serious buyer should ask directly before adopting this model, rather than assuming they’re automatically resolved.
- How researchers actually get vetted before gaining access to a client’s environment, and what ongoing monitoring exists once access is granted
- Where liability sits if a researcher’s activity causes unintended disruption during testing, and how that risk gets contractually allocated
- Whether sensitive findings and client environment details stay confined to the specific engagement rather than potentially informing a researcher’s work elsewhere
- How consistent quality actually is across a distributed pool compared to a smaller, more directly managed fixed team
Crowdsourcing has become an attractive model in the first place, sizing the substantial gap between the cybersecurity talent organizations need and the workforce currently available, a gap that makes accessing a wider distributed pool genuinely appealing regardless of the legitimate questions above.
Where Does a Dedicated Team Still Win Outright?
Crowdsourcing is not a universal replacement for a dedicated internal or vendor team, and being honest about where it falls short matters for a fair evaluation. Deep, ongoing institutional knowledge of a specific, complex environment tends to accumulate more naturally within a dedicated team that works with the same systems repeatedly over time, something a distributed pool of researchers, each potentially engaging with the environment for the first time, structurally cannot replicate as easily.
Highly sensitive environments with strict regulatory requirements around who can access specific data may also find a dedicated, more tightly controlled team easier to justify from a compliance standpoint, even if a crowdsourced model could theoretically deliver comparable technical coverage.
How Should a Business Actually Run a First Crowdsourced Engagement?
Starting with a defined, limited scope rather than the entire environment at once lets a business evaluate quality and process fit before committing more broadly. Establishing clear rules of engagement upfront- what’s in scope, what triggers immediate escalation, and how findings get reported and validated- matters more in a crowdsourced model than a traditional one, since the pool of people involved is inherently less familiar with unwritten organizational context a smaller internal team might otherwise assume.
FAQ
What does crowdsourced security testing actually change compared to a traditional team?
It draws on a much larger, more varied pool of researchers rather than a fixed team, often bringing broader specialized expertise and more diverse approaches to the same testing problem, with cost typically tied to actual findings rather than fixed team capacity.
What are the main risks businesses should evaluate before adopting a crowdsourced model?
Researcher vetting processes, how liability is allocated if testing causes unintended disruption, whether sensitive findings stay confined to the engagement, and consistency of quality across a distributed pool are all legitimate questions worth asking directly.
When does a dedicated internal or vendor team still make more sense than crowdsourcing?
Complex environments benefiting from deep accumulated institutional knowledge, and highly regulated environments with strict access control requirements, often still favor a dedicated, more tightly controlled team over a distributed crowdsourced pool.
How should a business structure its first crowdsourced testing engagement?
Starting with a limited, well-defined scope rather than the full environment, and establishing explicit rules of engagement upfront, helps evaluate the model’s fit before expanding to broader or more sensitive testing.